What Is an Enterprise MCP Gateway?
The Model Context Protocol (MCP), introduced by Anthropic in late 2024, is the standard protocol for connecting AI assistants to enterprise tools and data. An MCP gateway is a centralized entrypoint that sits between your AI systems and those tools, handling authentication, credential injection, tool curation, access policy, and audit logging for MCP interactions.
What makes a gateway "enterprise" is the governance layer on top of that routing function: SCIM-driven RBAC, per-agent identity, tamper-evident audit trails, compliance posture, and private-network access. MintMCP's platform addresses both questions: MCP Gateway answers "what tools can this AI system access?" and Agent Gateway adds "who is this agent, what authority does it have, and what has it done?"
MintMCP's platform addresses both questions through two connected product areas: MCP Gateway for governed tool and data connections, and Agent Gateway for first-class autonomous agent identity built on top of that foundation. The named primitives that make this concrete are Virtual MCPs (per-use-case endpoints with SCIM-driven membership and curated tool surfaces) and Agent Bundles (per-agent identity with scoped tools, M2M OAuth tokens, workload identity federation, and independent credential rotation and revocation).
Without a governed gateway, organizations face fragmented credentials across developer laptops, zero telemetry on what AI agents actually do, and uncontrolled access to internal systems that leaves security teams blind.
Key Takeaways
- Enterprise MCP governance requires more than routing: it requires per-role tool surfaces, per-agent identity, runtime controls, and visibility into both gateway traffic and local agent activity
- Performance-optimized gateways report low gateway overhead, but teams should distinguish gateway overhead, tool-call latency, end-to-end latency, and throughput when evaluating benchmarks
- Open-source options offer full control for teams avoiding vendor lock-in, with container-native approaches providing security through isolation
- Security vulnerabilities in the MCP ecosystem (clients, servers, and tooling) increase the need for enterprise gateway protection, including strong authentication, tool-level policy, audit logs, and isolation controls
How to Evaluate an Enterprise MCP Gateway
Before comparing vendors, establish which criteria matter most for your organization. These six dimensions separate purpose-built enterprise gateways from lighter-weight alternatives.
1. Deployment Model and Data Residency
Where does the gateway run, and where do credentials and audit data live? Managed SaaS-first platforms reduce operational burden but require trust in the vendor's data handling. Self-hosted or VPC deployments give infrastructure teams more control but require operating the runtime stack. Ask vendors: what regions are supported, what data leaves your environment, and what are the options for air-gapped or private-network deployment?
2. Identity and Access Control
Does the gateway integrate with your IdP through SSO and SCIM? Can directory groups drive tool-surface membership automatically? Virtual MCPs let you create separate governed endpoints for different teams, roles, or use cases, so an engineering team sees different tools than a sales team, even over the same underlying connector. See MintMCP's RBAC documentation for how this works in practice. For a broader view of MCP gateway architecture and governance model, that guide covers the access-control layer in depth.
3. Agent Identity and Non-Human Principals
Does each autonomous agent get its own identity, credentials, and audit trail, or does it inherit a human account or shared service key? As agent deployments grow, shared credentials become a liability: one compromised key affects every agent using it, and attribution becomes impossible. Ask vendors whether agents can authenticate independently and whether their credentials can be rotated or revoked without touching human accounts. See MCP security for enterprises for why this matters at scale.
4. Runtime Controls
What happens when an agent tries to access PII, exfiltrate credentials, or call a destructive tool? Monitoring after the fact is not enough. Ask vendors to name the enforcement mechanism: is it a managed detection policy, a declarative rule, or customer-authored logic? Each layer serves a different purpose, and the combination matters.
5. Visibility Model
Does monitoring cover only traffic routed through the gateway, or also local agent activity such as prompts, file access, and bash commands? Local coding agents like Claude Code and Cursor don't always route through a gateway, so gateway-only monitoring leaves a visibility gap. Ask whether the platform can cover both paths and whether it exports to your SIEM.
6. Compliance Posture
For regulated industries, verify: SOC 2 Type II audited status, HIPAA standards compliance with BAA availability, tamper-evident audit trails, SIEM export, and data residency options. Gateway-level controls provide valuable governance capabilities but do not guarantee regulatory compliance on their own. Verify specific attestations and contractual requirements with each vendor.
MCP Gateway Comparison: At a Glance
| Gateway | Best for | Deployment | Agent identity | Compliance |
|---|---|---|---|---|
| MintMCP | Enterprise employee and agent governance | Managed SaaS-first; VPC/self-hosted on request | Per-agent identity, bearer keys, M2M OAuth, workload identity federation | SOC 2 Type II audited; compliant with HIPAA standards; BAA available |
| TrueFoundry | Platform teams, unified LLM and MCP | Managed SaaS, hybrid, air-gapped | Not verified | Not verified |
| Bifrost | Latency-sensitive, OSS/self-hosted | OSS-first, self-hosted | Not verified | Not verified |
| Obot | Kubernetes-native, full data control | Self-hosted (Docker/K8s) or hosted dedicated GKE environment | Not verified | Not verified |
| Kong AI Gateway | Existing Kong infrastructure | Self-hosted or Konnect | Not verified | Not verified |
| Lasso Security | Runtime threat detection | OSS and commercial | Not verified | Not verified |
| Operant AI | Runtime defense, local and cloud | Enterprise platform | Not verified | Not verified |
| IBM ContextForge | Multi-gateway federation | Self-hosted | Not verified | Not verified |
| Traefik Hub | Existing Traefik infrastructure | Commercial | Not verified | Not verified |
| Microsoft Azure | Azure-first organizations | Open-source Kubernetes/AKS gateway or Azure API Management | Not verified | Not verified |
| Lunar.dev MCPX | Governance-focused teams | Open source; managed service and self-hosted Kubernetes options | Not verified | Not verified |
| Docker MCP Gateway | Container-native teams | Self-hosted | Not verified | Not verified |
"Not verified" cells reflect that these vendors are outside the detailed competitive reference used for this article. Verify current capabilities directly with each vendor before making a selection decision.
1. MintMCP Gateway: Enterprise MCP Governance
MintMCP Gateway is built for enterprise MCP governance, offering SOC 2 Type II audited security controls, compliance with HIPAA standards, and BAA availability. The platform transforms local MCP servers into production-ready services with managed hosting, OAuth protection, credential management, tool-level policy, and complete audit trails.
Best For
Mid-market and enterprise organizations, including regulated industries, that need governed MCP access for internal employees and internal agents.
What Makes MintMCP Different
MintMCP's approach addresses the core enterprise challenge of AI compliance concerns as a barrier to deployment. Its data-permissions-first architecture starts with SSO, SCIM-driven RBAC, IdP groups, Virtual MCPs, tool-level allowlisting, rule-based policy, and audit logs before enabling agents on top. The platform also supports OAuth brokering for STDIO and hosted MCP servers, helping teams move local servers into governed production environments.
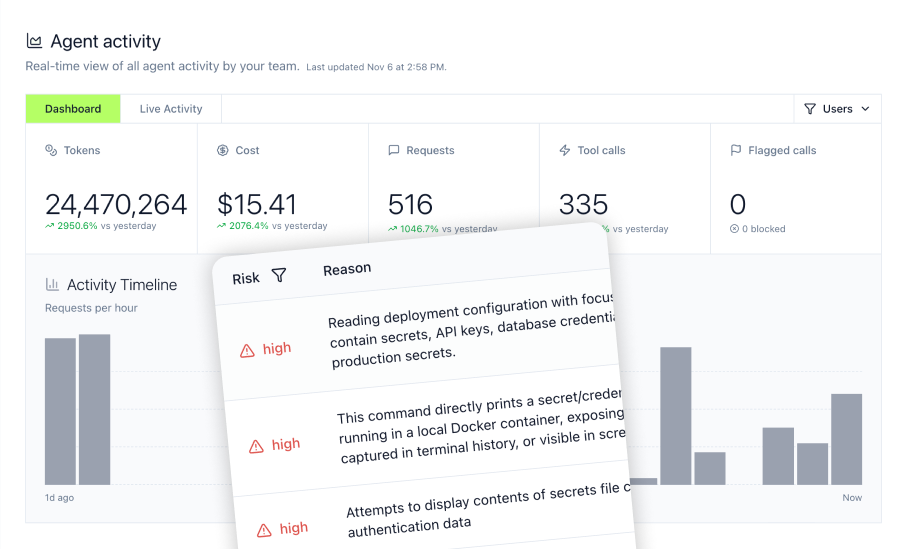
Agent Monitor adds visibility into supported coding-agent behavior, tracking MCP traffic as well as local non-MCP activity, tool calls, bash commands, and file operations from Claude Code, Claude Cowork, Cursor, Codex, and GitHub Copilot.
Engineering teams can connect AI assistants to internal databases through connectors like the Elasticsearch integration or Snowflake MCP Server, with governance policies enforced automatically.
Agent Gateway: Identity for Autonomous Agents
MintMCP's Agent Gateway builds on the MCP Gateway foundation by giving each autonomous agent its own non-human identity, scoped permissions, and independent credentials, separate from any human account or shared service key.
Each agent can authenticate via bearer keys, M2M OAuth tokens, or workload identity federation. Its access can be rotated or revoked independently without touching other agents or users. This matters because agents should not operate through whichever employee credential happens to be available. Per-agent identity solves that problem at the infrastructure level: each agent's credentials can be rotated or revoked independently, so no single human account becomes a dependency for agent operations.
The agent identities documentation covers the full authentication model. For a deeper treatment of the category, see the agent gateway definitive guide.
Guardrails: Runtime Controls for Agent Actions
MintMCP's Guardrails layer provides three named enforcement mechanisms:
Mint Guard provides managed detection policies for prompt injection, secrets, PII, and harmful content. It operates in Off, Monitoring, or Enforcing modes, so teams can observe before they block. See the Mint Guard documentation for policy details.
Rules provide declarative matching on tool name, arguments, or content. Supported actions include flag, block, ask, mask, or notify. Rules let teams encode specific enforcement logic without writing code.
Gateway Middleware lets teams author custom JavaScript running in a sandbox. It can integrate external DLP or classifier systems, redact content, transform tool arguments, or block calls based on custom logic. See the Gateway Middleware documentation for implementation details.
The buyer-language justification for this layer: non-technical users say "go do something" and an agent runs a destructive command without any human review. Runtime controls are the enforcement point that prevents that outcome.
Two-Layer Visibility: Gateway Traffic and Local Agent Activity
MCP Gateway governs traffic routed through governed MCP connections. Agent Monitor provides visibility into supported activity beyond gateway traffic: prompts, file access, bash commands, MCP tool calls, usage, and token costs from supported coding-agent environments including Claude Code, Claude Cowork, Cursor, Codex, and GitHub Copilot.
The distinction matters because local coding agents don't always route through a gateway. Gateway-only monitoring leaves a visibility gap for exactly the tools engineering teams use most. Agent Monitor can cover both paths for supported environments and supports SIEM export for centralized security visibility. For more on how these layers relate, see AI gateway vs MCP gateway vs agent gateway.
Key Features
- One-click STDIO deployment with automatic hosting and lifecycle management
- OAuth 2.0, SAML, SSO, and SCIM-driven RBAC for enterprise authentication and authorization
- Virtual MCPs with per-use-case endpoints, SCIM-driven membership, role-based access control, and granular tool permissions
- Agent Bundles with bearer keys, M2M OAuth tokens, and workload identity federation for per-agent identity, scoped tool access, and independent credential rotation and revocation, so each agent is independently identifiable, auditable, and revocable
- Mint Guard for managed detection of prompt injection, secrets, and PII, with Off, Monitoring, and Enforcing modes, plus declarative Rules that match on tool name, arguments, or content and can flag, block, ask, mask, or notify
- Gateway Middleware for customer-authored JavaScript running in a sandbox, enabling DLP integrations, external classifier calls, content redaction, and custom enforcement logic
- Tool-update policy: approve or auto-allow new tools when upstream MCP servers change their tool surface, preventing silent capability expansion
- Tamper-evident audit trails, centralized observability, and credential management
Deployment
Managed SaaS-first, with VPC/self-hosted deployment on request
Learn More: mintmcp.com/mcp-gateway
2. TrueFoundry MCP Gateway
TrueFoundry delivers performance-focused infrastructure for high-volume production deployments, with published MCP Gateway materials reporting approximately 10ms latency under load and 350+ requests per second on a single vCPU (per TrueFoundry's published MCP Gateway materials; these are vendor-reported benchmark figures and should be verified against the current test setup before use as a selection criterion). The platform unifies LLM and MCP tool management in a single control plane, simplifying infrastructure for platform engineering teams.
Where TrueFoundry Fits Best
High-throughput applications where latency directly impacts user experience and organizations requiring unified LLM and MCP governance.
Performance Architecture
TrueFoundry's architecture is designed for enterprise-scale traffic without extensive configuration overhead. The platform reports hundreds of requests per second with low latency, making it relevant for production deployments. The unified billing and observability for LLMs and MCPs reduces operational overhead.
Key Features
- Low-latency gateway performance with no tuning required
- OAuth 2.0 Identity Injection with On-Behalf-Of authentication
- Virtual server abstraction that presents multiple backend servers as a single endpoint
- Unified management of LLM routing and MCP tool access
Considerations
TrueFoundry is well suited to platform engineering and ML platform teams that want unified LLM and MCP infrastructure. MintMCP's Virtual MCPs address the same N-to-M integration problem through per-use-case endpoints with SCIM-driven membership and curated tool surfaces; evaluate which abstraction fits your access-control model. Teams prioritizing IT and security-led employee governance should also evaluate whether they need MintMCP-specific primitives such as SCIM-driven Virtual MCPs, Agent Bundles with M2M auth, hosted MCP connectors, tool-update policy, and MintMCP's two-layer visibility model combining MCP Gateway governance with Agent Monitor coverage beyond gateway traffic.
Deployment
Managed SaaS, on-premise, or air-gapped environments
3. Bifrost
Bifrost is a performance-focused MCP gateway, with published benchmarks reporting approximately 11 microsecond gateway overhead at 5,000 requests per second (results are workload- and configuration-dependent; this figure reflects gateway overhead only, not end-to-end or tool-call latency). Built in Go, the open-source platform offers enterprise-oriented capabilities without licensing costs.
Where Bifrost Fits Best
Latency-sensitive applications and teams requiring open-source flexibility with minimal gateway overhead.
Performance Characteristics
Bifrost's in-memory security model achieves low gateway overhead through stateless authentication and rate limiting. The dual MCP client/server architecture enables zero-configuration deployment starting in 30 seconds, with published benchmarks showing materially higher throughput versus some alternative gateways under load. Results are workload- and configuration-dependent.
Key Features
- Approximately 11 microsecond gateway overhead in published benchmarks
- Dual MCP client/server architecture
- Zero-configuration deployment starting in 30 seconds
- Open-source Apache 2.0 license; verify current enterprise edition availability and terms
Considerations
Bifrost is OSS-first and self-hosted-first. Teams that want a managed SaaS-first gateway with hosted MCP connectors, SCIM-driven membership, per-use-case Virtual MCPs, Agent Bundles, and centralized employee and agent governance may prefer MintMCP.
Deployment
Open-source (Apache 2.0) with enterprise edition available
4. Docker MCP Gateway
Docker MCP Gateway brings familiar container orchestration workflows to MCP server management. With access to the Docker MCP Catalog featuring pre-built servers (per Docker's documentation; catalog size changes frequently), teams already using Docker can add MCP capabilities without learning new tooling.
Where Docker Gateway Fits Best
Organizations with existing Docker and container infrastructure seeking container-native security and familiar deployment workflows.
Container-Native Security
The container-based approach provides security through isolation. CVE-2025-6514 separately affected mcp-remote versions 0.0.5 through 0.1.15 and was fixed in v0.1.16; upgrading to v0.1.16 or later is the appropriate remediation. Container isolation with CPU and memory limits can help reduce resource exhaustion risk, while signed images can strengthen supply-chain controls.
Key Features
- Container isolation for secure MCP server deployments
- Docker Compose integration for orchestration
- Signed container images
- Access to a pre-built MCP server catalog
Deployment Considerations
The container-based approach can add operational and runtime overhead compared to purpose-built managed gateways. However, teams prioritizing security through container isolation and familiar workflows may find this acceptable.
Considerations
Docker MCP Gateway fits teams that already want to operate Docker and container infrastructure. Teams looking to avoid managing connector runtimes, scaling, and container operations should compare it with MintMCP's managed SaaS-first deployment and hosted MCP connectors.
Deployment
Self-hosted with Docker Desktop or Docker Engine; Docker Compose can run the gateway as part of a containerized application
5. Lasso Security MCP Gateway
Per Lasso's documentation, the open-source gateway prioritizes threat detection over raw performance. Lasso Security implements security controls across AI, MCP, and API layers.
Where Lasso Fits Best
Security-conscious organizations and high-risk deployment environments requiring real-time threat detection and MCP server reputation scoring.
Security-Focused Architecture
Per Lasso's documentation, the platform provides real-time prompt injection detection and blocking, with MCP server reputation scoring that identifies risky tools before they cause incidents. The plugin-based architecture enables custom security extensions tailored to specific organizational requirements.
Key Features
- Real-time prompt injection detection and blocking, per Lasso's documentation
- MCP server reputation scoring with automatic blocking, per Lasso's documentation
- Plugin-based architecture for custom security extensions, per Lasso's documentation
- Added latency depends on enabled inspection depth and deployment architecture
Considerations
Lasso emphasizes MCP threat detection and inspection. Teams should also evaluate whether they need SCIM-driven RBAC, per-use-case tool surfaces, audit logs, credential management, hosted MCP connectors, and agent identity governance as first-class gateway capabilities.
Deployment
Open-source; verify current commercial platform availability and terms
6. Lunar.dev MCPX
Lunar.dev MCPX provides purpose-built governance capabilities with granular access control at global, service, and tool levels. Per Lunar.dev's published documentation, the platform reports approximately 4ms p99 latency while maintaining audit logs and policy enforcement; independently verify before selection.
Where MCPX Fits Best
Organizations prioritizing centralized governance and RBAC with integration across LLM, MCP, and API traffic.
Governance Approach
MCPX addresses regulatory complexity through centralized policy enforcement that simplifies governance without requiring per-tool configuration. Per Lunar.dev's documentation, the platform provides granular access control across multiple hierarchy levels with tool customization for improved LLM accuracy.
Key Features
- Granular access control across multiple hierarchy levels
- Tool customization for improved LLM accuracy, per Lunar.dev's documentation
- Comprehensive audit logs with tamper-resistant trail, per Lunar.dev's documentation
- Integration with Lunar AI Gateway for end-to-end coverage
Considerations
MCPX is a governance-oriented MCP gateway. MintMCP provides tamper-evident audit trails as well; evaluate both platforms' audit architecture against your compliance requirements. Teams should also compare MCPX's access-control model with MintMCP's data-permissions-first approach, including SCIM-driven Virtual MCPs, Agent Bundles with M2M auth, hosted MCP connectors, and two-layer visibility combining MCP Gateway governance with Agent Monitor coverage beyond gateway traffic.
Deployment
Open source, with managed service and self-hosted Kubernetes enterprise options; verify current deployment options, pricing, and tier structure with Lunar.dev directly.
7. IBM ContextForge
IBM ContextForge provides a multi-gateway federation architecture for large enterprises, with protocol bridging for REST/gRPC to MCP conversion, per IBM's documentation. Teams evaluating ContextForge should verify current capabilities, support model, and production readiness against their requirements.
Where ContextForge Fits Best
Large distributed enterprises requiring multi-gateway federation and protocol bridging for REST/gRPC to MCP conversion.
Federation Architecture
Per IBM's documentation, ContextForge's multi-gateway federation with auto-discovery provides virtual MCP servers combining multiple backend servers. The platform includes OpenTelemetry observability support for comprehensive monitoring.
Key Features
- Federation architecture with auto-discovery, per IBM's documentation
- Virtual server abstraction combining multiple backend servers
- Protocol bridging for REST/gRPC to MCP conversion
- OpenTelemetry observability support
Important Consideration
ContextForge may appeal to teams that need open-source federation and protocol bridging. Organizations should evaluate the maturity, support model, and operational requirements against their production governance needs.
Considerations
A self-hosted federation layer can give infrastructure teams more control, but it may require the customer to operate more of the gateway, database, and runtime stack. MintMCP addresses this with managed SaaS-first deployment, hosted MCP connectors, SCIM-driven access, audit logs, and credential management.
Deployment
Self-hosted; verify current backend and infrastructure requirements.
8. Obot Platform
Obot combines gateway functionality with MCP catalog management and agent orchestration in a Kubernetes-native platform.
Where Obot Fits Best
Teams wanting a complete platform rather than standalone gateway, with emphasis on catalog management and orchestration capabilities.
Platform Philosophy
Obot's approach emphasizes that enterprise MCP adoption requires more than just a gateway. Teams need catalog management, documentation, and orchestration capabilities working together through a central control plane.
Key Features
- Built-in MCP Catalog with discovery and documentation
- Enterprise IdP support for Okta and Microsoft Entra
- Agent orchestration framework for turning MCP servers into AI agents, per Obot's documentation
- Central control plane for IT policy management
Considerations
Obot supports OSS/self-hosted deployment, with Docker for development and Kubernetes for production, and also offers a hosted MCP Gateway on a dedicated GKE environment. Teams that want a managed SaaS-first gateway, hosted MCP connectors, SCIM-driven Virtual MCPs, and Agent Bundles for per-agent identity may find MintMCP a closer fit.
Deployment
Self-hosted on Kubernetes or Obot-hosted in a dedicated GKE environment; verify current enterprise support availability and terms
9. Kong AI Gateway
Kong AI Gateway extends Kong API Gateway with MCP capabilities, allowing organizations to expose existing REST APIs as MCP servers. Kong AI Gateway added OAuth 2.1 implementation for MCP traffic in version 3.12; the same release also added LLM-as-a-Judge for LLM prompt-response evaluation, but that capability applies to LLM traffic rather than MCP traffic (version-specific; verify current release notes).
Where Kong Fits Best
Organizations with existing Kong infrastructure investments seeking unified API and MCP management through a single platform.
Integration Advantage
Kong leverages API gateway infrastructure, providing a familiar path for organizations already managing APIs through the platform. The centralized OAuth plugin secures MCP servers through the existing gateway layer.
Key Features
- MCP server generation from REST APIs
- Centralized OAuth plugin for MCP servers
- LLM-as-a-Judge policy for LLM prompt-response evaluation in the broader AI Gateway, not MCP traffic
- Unified API and MCP management through single platform
Considerations
An API gateway extension can fit teams already standardized on Kong, but it may not provide MCP-specific governance primitives such as SCIM-driven Virtual MCPs, Agent Bundles, tool-update policy, STDIO/hosted-server OAuth brokering, or two-layer visibility across MCP and local agent activity.
Deployment
Hybrid or fully self-hosted depending on Kong deployment model; verify current deployment options
10. Traefik Hub MCP Gateway
Traefik Hub extends Traefik reverse proxy infrastructure with MCP gateway capabilities. Its security architecture provides defense-in-depth across multiple security layers.
Where Traefik Fits Best
Teams already using Traefik for API management seeking to add MCP capabilities as middleware layers.
Middleware Philosophy
For organizations already routing traffic through Traefik, adding MCP capabilities requires minimal infrastructure changes. Per Traefik Hub's documentation, the gateway supports On-Behalf-Of (OBO) Authentication and Task-Based Access Control (TBAC).
Key Features
- On-Behalf-Of (OBO) Authentication with OAuth 2.0 token exchange, per Traefik Hub's documentation
- Task-Based Access Control (TBAC) for dynamic authorization, per Traefik Hub's documentation
- OpenTelemetry metrics and traces for MCP operations
- Cloud-native design leveraging existing Traefik infrastructure
Considerations
Traefik Hub is a natural fit for teams already using Traefik as an infrastructure layer. Teams evaluating MCP-specific governance should compare it with MintMCP capabilities such as managed hosted connectors, Virtual MCPs, Agent Bundles, credential management, and tool-update policy.
Deployment
Commercial; verify current licensing and deployment options.
11. Microsoft Azure MCP Solutions
Microsoft offers two relevant MCP gateway approaches: the open-source Microsoft MCP Gateway for Kubernetes environments, including AKS, and MCP server governance through Azure API Management. These are separate offerings rather than two deployment modes of a single gateway. Native Microsoft Entra ID integration provides authentication options for Microsoft-centric organizations.
Where Azure Gateway Fits Best
Azure-first organizations prioritizing ecosystem integration with native Entra ID authentication and Azure Monitor observability.
Ecosystem Integration
Across these Azure-based options, integration with Entra ID, Azure Monitor, and Application Insights provides familiar deployment paths for organizations committed to Microsoft's cloud ecosystem. Microsoft's open-source MCP Gateway provides session-aware routing for Kubernetes environments, while Azure API Management provides separate capabilities for exposing and governing MCP servers.
Key Features
- Native Entra ID integration for authentication
- Azure Monitor and App Insights for observability
- Session-aware routing in Microsoft's open-source Kubernetes MCP Gateway
- Open-source MCP Gateway for Kubernetes including AKS, plus separate Azure API Management MCP server governance capabilities
Considerations
Azure MCP solutions fit Azure-first infrastructure strategies. Teams operating across multiple AI assistants and data platforms should also evaluate whether they need vendor-neutral governance across Claude, Cursor, ChatGPT, Gemini, and Copilot, plus MintMCP capabilities such as Virtual MCPs, Agent Bundles, hosted MCP connectors, and Agent Monitor coverage.
Deployment
Open-source MCP Gateway on Kubernetes including AKS, or separate MCP server governance through Azure API Management; verify current deployment options
12. Operant AI
Operant AI focuses on runtime threat detection across local and cloud agent environments, per their published documentation. Verify current capabilities before selection.
Where Operant Fits Best
Organizations prioritizing threat detection and facing sophisticated threats or operating in adversarial environments.
Research-Driven Approach
Per Operant AI's published security research, the platform targets emerging AI-specific threats through a Discovery, Detection, Defense approach. The research covers attack vectors including zero-click AI exploits, with inline redaction and dynamic control capabilities.
Key Features
- AI-native threat identification for MCP traffic, per Operant AI's published research
- Inline redaction and dynamic control capabilities, per Operant AI's published research
- Published security research on securing MCP
- Runtime defense across local and cloud agent environments
Considerations
Operant AI is a strong fit for teams prioritizing runtime defense and threat detection. Teams should also evaluate whether they need MintMCP's broader enterprise governance layer, including SSO, SCIM-driven RBAC, tool-level allowlisting, credential management, Virtual MCPs, Agent Bundles, and audit logs.
Deployment
Enterprise platform; verify current pricing and deployment options.
Making Your Choice: Selection Criteria
Compliance Requirements
If your organization operates in regulated industries, SOC 2 Type II audited security controls, compliance with HIPAA standards, and BAA availability can reduce procurement friction. MintMCP Gateway offers both, along with audit logs, role-based access control, and governance controls for internal employee and agent access. Understanding MCP gateway architecture and governance model helps frame these compliance requirements.
Performance Needs
For latency-sensitive applications, the performance gap between gateways matters, but teams should compare the same metric type across vendors:
- Gateway overhead: Bifrost (approximately 11 microsecond overhead in published benchmarks)
- Low gateway latency: TrueFoundry (approximately 10ms per published MCP Gateway materials), Lunar.dev (approximately 4ms p99 gateway overhead per Lunar.dev's published documentation; verify independently)
- Container or cloud deployment overhead: Docker and Azure vary by deployment model
- Security inspection overhead: Lasso and Operant AI vary based on enabled inspection depth and deployment architecture
Deployment Model
Your infrastructure preferences narrow the field quickly:
- Managed SaaS-first: MintMCP, Lunar.dev
- Hybrid managed SaaS and self-hosted: TrueFoundry, Kong
- Self-hosted or OSS-first: Docker, Lasso, IBM ContextForge, Obot, Bifrost
- Ecosystem extension: Kong, Traefik, Microsoft Azure
Cost Considerations
Open-source options such as Bifrost, Docker, Lasso, IBM ContextForge, and Obot can reduce licensing costs but require infrastructure investment and operational expertise. Managed platforms trade higher subscription costs for reduced operational burden, often the better choice when enterprises are building numerous AI agent prototypes simultaneously.
Deploy Enterprise AI with Confidence
Deploying MCP at scale requires more than protocol support. It requires per-role tool surfaces through Virtual MCPs, per-agent identity through Agent Gateway, runtime enforcement through Mint Guard and Rules, and visibility into both gateway traffic and local agent activity through Agent Monitor.
MintMCP Gateway provides a governance stack in a managed SaaS-first deployment, with SOC 2 Type II audited security controls, compliance with HIPAA standards, BAA availability, hosted MCP connectors, credential management, tool-level policy, and tamper-evident audit trails.
Whether you're securing access to Snowflake data warehouses, Elasticsearch knowledge bases, or custom enterprise tools, MintMCP provides the infrastructure that makes AI deployment practical, governed, and secure.
For a deeper understanding of MCP gateway architecture, see our guide to understanding MCP gateways.
Ready to transform your AI infrastructure? Visit mintmcp.com to schedule a demo and see how MintMCP Gateway can accelerate your enterprise AI deployment.
Frequently Asked Questions
What is an MCP gateway and why do enterprise engineering teams need one?
An MCP gateway centralizes authentication, observability, and governance for Model Context Protocol servers. Without a gateway, organizations face fragmented credentials, zero visibility into AI agent behavior, and uncontrolled access to internal systems. As enterprises require tech stack upgrades for AI agent deployment, gateways have become essential infrastructure.
What is the difference between an MCP gateway and an API gateway?
An API gateway governs HTTP traffic between services. An MCP gateway governs tool-call traffic between AI systems and enterprise data sources, with MCP-specific primitives like tool curation, credential injection, per-agent identity, and tool-update policy that API gateways don't provide natively. For a detailed comparison, see AI gateway vs MCP gateway vs agent gateway.
What is the difference between an MCP gateway and an agent gateway?
An MCP gateway answers "what tools can this AI system access?" An agent gateway adds "who is this agent, what authority does it have, what credentials does it use, and what has it done?" MintMCP's Agent Gateway builds on its MCP Gateway foundation to answer both questions. Each autonomous agent gets its own non-human identity, scoped permissions, and independent credentials rather than inheriting a human account or shared service key.
Do enterprise MCP gateways work with Claude, Cursor, ChatGPT, Gemini, and Copilot?
Yes. MintMCP's MCP Gateway supports Claude, Cursor, ChatGPT, Gemini, and Copilot through Virtual MCPs: governed endpoints that each AI client connects to with a single configuration rather than separate per-server setup. Agent Monitor also covers local activity from Claude Code and other supported coding agents beyond gateway traffic.
How do MCP Gateways ensure compliance with regulations like SOC 2 and GDPR?
Governed gateways provide audit trails of MCP interactions, role-based access control, and comprehensive logging. MintMCP Gateway is SOC 2 Type II audited and supports deployments compliant with HIPAA standards, with BAA availability, while other platforms offer varying compliance features. Organizations should verify specific attestations, certifications, and contractual requirements because gateway-level controls provide valuable governance capabilities but do not guarantee regulatory compliance on their own.
What security features should enterprise engineering teams prioritize?
Essential security capabilities include OAuth 2.0/SAML authentication, SSO, SCIM-driven RBAC, audit logging, tool-level allowlisting, rule-based policy, credential management, and real-time monitoring. Advanced features like prompt injection detection (Lasso Security, per their documentation) and threat detection (Operant AI, per their published research) address emerging risks. Container isolation (Docker) and signed images provide additional security layers for MCP deployments.
What compliance certifications should an enterprise MCP gateway have?
Look for SOC 2 Type II audited status, HIPAA standards compliance with BAA availability, tamper-evident audit trails, SIEM export, and data residency options. MintMCP is SOC 2 Type II audited and compliant with HIPAA standards, with BAA availability for customers handling protected health information.
Can MCP Gateways help manage costs and monitor AI tool usage?
Yes. Gateways provide visibility into which teams use which tools, enabling accurate cost allocation and usage optimization. MintMCP's Agent Monitor includes usage and token cost tracking across supported AI clients and agents. This visibility matters as organizations scale from pilots to production, with observability viewed as essential for AI infrastructure.
How does an MCP Gateway facilitate integration with existing enterprise data sources?
MCP gateways provide connectors and protocol bridging to enterprise systems. For example, MintMCP offers pre-built integrations with Elasticsearch, Snowflake, and databases, allowing AI assistants to query internal data with proper governance. IBM ContextForge adds REST/gRPC-to-MCP conversion for legacy system access, per IBM's documentation.
What role does an MCP Gateway play in transforming local AI projects into production services?
Many MCP servers are STDIO-based and can be difficult to deploy at scale. Gateways transform these local tools into production services by adding hosting, authentication, monitoring, and high availability. MintMCP Gateway provides one-click deployment, OAuth brokering, hosted MCP connectors, credential management, and audit logs that reduce infrastructure setup, which is essential for moving beyond.