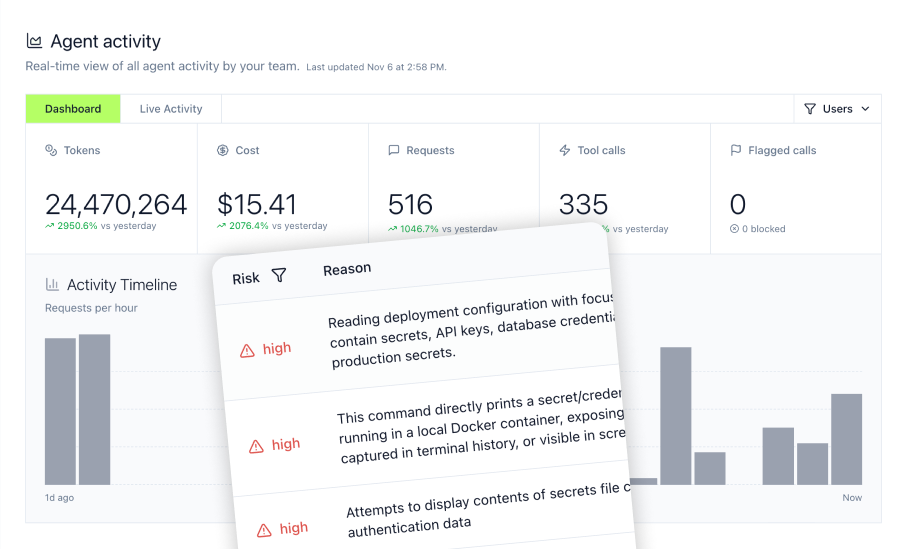
Quick answer: An MCP gateway sits between your AI agents and the tools they access, databases, APIs, internal systems, centralizing authentication, access control, credential management, and audit. For AI startups, the right gateway determines whether you can move fast without accumulating credential debt, configuration sprawl, or security gaps that block enterprise sales.
This guide covers: 10 MCP gateway options for startups in 2026, organized by deployment model and use case, from managed SaaS-first platforms to open-source self-hosted options.
Today, most AI startups hit the same wall: developers configure MCP servers independently across laptops, agents run on whoever's OAuth session happens to be available, and security teams have no way to see what those agents are actually doing. One engineer owns all the API keys. One compromised credential is keys to the kingdom.
The Model Context Protocol has become a standard for AI-tool communication, backed by Anthropic, OpenAI, Google, and Microsoft. MCP adoption has accelerated across the industry, but the protocol alone doesn't solve security, governance, or scaling challenges that startups face. Most organizations lack adequate visibility into what agents are doing, and even fewer have the controls to stop them when something goes wrong. Choosing the right gateway is critical for both security and business success.
We reviewed the leading MCP gateway options available to AI startups in 2026, evaluating deployment model, security posture, governance capabilities, and startup fit.
Key Takeaways
- Open-source options like Docker, Obot, and Lasso provide full control without licensing costs for teams with DevOps expertise
- Performance leaders should be evaluated by the specific metric they publish, since gateway overhead, tool-call latency, end-to-end latency, and throughput are not interchangeable
- Pricing ranges from free open-source options to custom enterprise plans, with startup programs offering significant credits
- MCP-specific security risks including tool poisoning, rug-pull updates, and prompt injection through tool responses require gateway-level controls, not just protocol support
- Security vulnerabilities in MCP servers require gateway protection, and research has identified command injection flaws, unrestricted network access, and file leakage risks across implementations
How to Choose an MCP Gateway for Your Startup
Before evaluating vendors, align on the five criteria that matter most for startups.
1. Deployment model first
Managed SaaS vs. self-hosted is the first decision. Startups without dedicated DevOps should default to managed. Self-hosted gives infrastructure control but adds operational burden: you own uptime, upgrades, and security patching.
2. Internal governance vs. external integration
Some gateways (Composio, Zapier) are optimized for connecting agents to external SaaS tools. Others (MintMCP, Runlayer, Natoma) are optimized for governing internal employee and agent access to company systems. These are different problems. Evaluate which one you actually have.
3. Agent identity from day one
If you're running autonomous agents, each agent should have its own credentials, not inherit a developer's OAuth session. Evaluate whether the gateway supports per-agent identities with independent rotation and revocation. See RBAC and agent identities for what this looks like in practice.
4. Compliance runway
If you're selling to regulated industries, SOC 2 Type II audit readiness and HIPAA documentation matter before your first enterprise deal, not after. Evaluate audit trail format and export capability before you need it.
5. Visibility beyond the gateway
Some gateways only log traffic that routes through them. If your developers run Claude Code or Cursor locally, you need visibility into that activity too. A gateway that only sees centralized traffic leaves a significant blind spot.
MCP-Specific Security Risks Startups Need to Govern
MCP introduces a category of security risks that traditional API security doesn't cover. Four threats matter most for startups.
Tool poisoning. Malicious instructions embedded in tool descriptions that agents read as trusted input. Agents treat tool descriptions as authoritative context, which makes them an injection surface. Mint Guard provides managed detection policies for this category.
Rug-pull updates. An MCP server changing its tool definitions after your team approved it. Without a tool-update policy, agents gain access to new or modified tools automatically. MintMCP's tool-update policy lets you require approval before agents gain access to upstream tool changes.
Prompt injection through tool responses. Tool outputs that contain instructions designed to redirect agent behavior. This is distinct from tool poisoning: the attack surface is the response, not the description. Gateway Middleware supports customer-authored logic for inspecting and transforming tool responses before they reach the agent.
Credential sprawl. Agents inheriting developer OAuth sessions or shared API keys, creating single points of failure. Agent Bundles address this directly: each agent gets its own credentials, independently rotatable and revocable. For a broader treatment of these risks, see AI agent security risks and the agent security guardrails guide.
One documented example: CVE-2025-6514 identified a command-injection vulnerability in the mcp-remote npm package, patched in v0.1.16. Enterprise gateways provide the security layer these tools require for production use.
MCP Gateway Comparison: At a Glance
| Gateway | Best for | Deployment | Key differentiator | Compliance |
|---|---|---|---|---|
| MintMCP | Internal employee and agent governance | Managed SaaS-first | Virtual MCPs, Agent Bundles, Agent Monitor | SOC 2 Type II audited, HIPAA |
| Composio | Developer teams, external integrations | Managed cloud, VPC | Large managed integration library | SOC 2 Type II audited |
| Runlayer | IT/Security/AIOps and platform engineering | Managed SaaS plus self-hosted | Internal governance, hybrid deployment | Not verified |
| Obot | Open-source and managed MCP deployment | Managed cloud + self-hosted (Docker/K8s) | OSS-first, full data control | Not verified |
| Bifrost | Technical teams, low-overhead routing | Self-hosted-first | Ultra-low gateway overhead (verify current figures) | Not verified |
| TrueFoundry | ML platform teams, unified LLM and MCP | Managed SaaS plus hybrid | Unified LLM and tool control plane | Not verified |
| Portkey | Developer and platform teams | Managed SaaS, OSS, self-hosted | LLM gateway plus MCP, broad model access | SOC 2 Type II audited |
| Docker MCP Gateway | Container-native teams | Self-hosted | Container-per-server isolation | Open source |
| Lasso Security | Security-first, regulated data | Self-hosted | Real-time threat detection, PII masking | MIT license (verify current) |
| IBM ContextForge | Distributed and federated MCP infrastructure | Self-hosted | Multi-gateway federation, protocol bridging | Apache 2.0 |
Deployment options, compliance status, and feature availability change. Verify current details with each vendor before committing.
1. MintMCP: Enterprise MCP Infrastructure in Minutes
MintMCP transforms local MCP servers into production-ready services with OAuth protection and enterprise monitoring. As a SOC 2 Type II audited MCP platform and an official Cursor Hooks partner, MintMCP addresses the core barrier to MCP adoption: the gap between developer experimentation and production deployment.
What Makes MintMCP Different
MintMCP starts with a data-permissions-first architecture: SSO, SCIM-driven RBAC, IdP groups, Virtual MCPs, tool-level policy, and audit logs are established before agents are enabled on top. Its MCP Gateway supports OAuth brokering for stdio and hosted MCP servers, hosted MCP connectors run by MintMCP, and per-use-case endpoints through Virtual MCPs.
Runtime controls run through three layers: Mint Guard for managed detection policies covering prompt injection, secrets, PII, and harmful content; Rules for declarative matching with flag, block, mask, or notify actions; and Gateway Middleware for customer-authored logic in a JS sandbox, including integrations with external DLP tools and classifiers.
Key Capabilities
- OAuth brokering for stdio and hosted MCP servers, with centralized credential injection
- SOC 2 Type II audited controls, compliant with HIPAA standards, penetration testing, encryption in transit and at rest, and complete audit trails
- SSO and SCIM-driven RBAC with granular tool access control by role
- Virtual MCPs for per-use-case endpoints with SCIM-driven membership and curated tool surfaces
- Agent Bundles with bearer keys, M2M OAuth tokens, and workload identity federation; each agent gets its own credentials, independently rotatable and revocable
- Tool-update policy: approve new upstream tools before agents gain access, or auto-allow, controlled per Virtual MCP
- Real-time agent activity visibility through Agent Monitor, covering tool calls, bash commands, and file access from Claude Code, Cursor, and other coding agents, including activity outside MCP Gateway traffic
- Hosted MCP connectors run by MintMCP, including connectors for Snowflake, Elasticsearch, and Gmail
For startups running AI coding agents, Agent Monitor complements the Gateway by providing visibility into tool calls, bash commands, and file operations from Claude Code, Cursor, and Copilot, including activity that doesn't route through the MCP Gateway. Coverage varies by client and hook phase.
Best For: Startups requiring rapid enterprise deployment with compliance from day one.
Pricing: Enterprise plans available; request pricing based on team size and deployment needs.
2. Composio
Composio provides a large managed integration library that enables startups to connect AI agents to enterprise tools. With extensive pre-built integrations and unified authentication, the platform reduces integration complexity for development teams.
What Makes Composio Different
Composio's library of pre-built integrations comes with unified authentication handled automatically, reducing the need to build custom OAuth flows. The platform is oriented toward developer and AI engineering teams building agentic applications.
Key Capabilities
- An extensive managed integration library with unified authentication (verify current catalog size at composio.dev)
- SOC 2 Type II audited controls with RBAC (verify current certification status at composio.dev)
- Startup program offering credits
Tradeoffs to Consider
Composio is oriented toward developer and AI engineering teams building external customer-facing products. Startups that need internal employee and agent governance should verify whether Composio's SSO, SCIM-driven RBAC, Virtual MCP Bundles, tool-level policy, and per-agent identity governance match their internal access-control requirements.
Best For: Startups prioritizing broad integration coverage without dedicated DevOps resources.
Pricing: Free tier available; paid plans start at entry-level pricing.
3. Runlayer
Runlayer targets IT, security, AIOps, and platform engineering teams governing internal employees and agents. Its hybrid deployment model supports both managed SaaS and self-hosted options on customer infrastructure.
What Makes Runlayer Different
Runlayer's hybrid deployment model gives teams the option to run the gateway on their own infrastructure while still benefiting from a managed control plane. The platform is oriented toward internal governance use cases similar to MintMCP.
Key Capabilities
- Managed SaaS plus self-hosted deployment on customer infrastructure (verify current deployment options at runlayer.com)
- Internal employee and agent governance orientation
- Enterprise identity provider support (verify current IdP integrations at runlayer.com)
Tradeoffs to Consider
Runlayer and MintMCP overlap closely in internal MCP and agent governance. When comparing the two, evaluate specific product differences: MintMCP's Virtual MCPs provide per-use-case endpoints with SCIM-driven membership and curated tool surfaces, and Agent Bundles provide per-agent identity with M2M auth and independent credential rotation and revocation. Verify whether Runlayer's current feature set matches your requirements for those specific primitives.
Best For: Startups and scale-ups that want internal governance with the option to self-host on their own infrastructure.
Pricing: Contact for current pricing.
4. Bifrost
Bifrost represents a performance-focused approach to MCP gateway architecture, built in Go for high throughput. The platform reports low gateway overhead; verify current published figures directly with the Bifrost team before relying on any specific number.
What Makes Bifrost Different
The gateway delivers dual functionality as both an AI gateway for LLM routing and an MCP gateway for tool orchestration. This unified approach can reduce the need for separate infrastructure components.
Key Capabilities
- Ultra-low gateway overhead (verify current published figures)
- Unified interface to multiple LLM providers plus native MCP support
- Apache 2.0 license with complete transparency
Tradeoffs to Consider
Bifrost is OSS-first and self-hosted-first. That can work well for technical teams that want to operate the gateway themselves, but teams looking for managed SaaS-first deployment, hosted MCP connectors, SSO and SCIM-driven RBAC, Virtual MCPs, Agent Bundles, and centralized audit may find MintMCP better aligned with internal governance needs.
Best For: Technical startups building real-time applications where latency impacts user experience.
Pricing: Free and open-source.
5. TrueFoundry
TrueFoundry provides a complete AI infrastructure platform that includes MCP gateway capabilities alongside model serving and MLOps management. The platform emphasizes low-latency performance and high throughput in published materials.
What Makes TrueFoundry Different
The platform consolidates LLM deployment, MCP tool orchestration, and observability into a single control plane. In-memory authentication and rate limiting are described in TrueFoundry's published materials as designed to reduce database overhead. Verify current architecture details at truefoundry.com.
Key Capabilities
- Low latency with production-grade performance
- Unified control plane for models and tools
- Federated SSO with enterprise identity providers (verify current IdP support at truefoundry.com)
- Flexible deployment options including VPC and on-premises (verify current deployment options at truefoundry.com)
Tradeoffs to Consider
TrueFoundry is a broader AI infrastructure and ML platform. Startups that specifically need MCP governance should compare its control plane against MintMCP capabilities such as Virtual MCPs, Agent Bundles with M2M auth, hosted MCP connectors, OAuth brokering for stdio and hosted servers, and tool-update policy.
Best For: Startups building comprehensive AI platforms wanting consolidated infrastructure.
Pricing: Free tier available; contact for paid plans.
6. Docker MCP Gateway
Docker MCP Gateway brings MCP deployment to familiar container orchestration. For startups already running Docker infrastructure, this gateway integrates with existing CI/CD workflows without additional learning curve.
What Makes Docker Different
Every MCP server runs in isolated containers. Signed images can support supply chain controls for sensitive deployments. Verify current resource-limit and image-signing capabilities directly with Docker.
Key Capabilities
- Container isolation with configurable resource limits
- Docker Compose integration for familiar workflows (verify current integration details at docs.docker.com)
- Supply chain security through signed images
- Familiar workflow for Docker-native teams
Tradeoffs to Consider
Docker MCP Gateway fits teams that want to package and run MCP servers inside their existing container environment. Teams still need to evaluate identity governance, SSO and SCIM-driven RBAC, tool-level allowlisting, audit logs, hosted connector operations, Virtual MCPs, and Agent Bundles if they need a managed governance layer for internal employees and agents.
Best For: Container-native teams valuing ecosystem familiarity and operational consistency.
Pricing: Free and open-source.
7. Obot Platform
Obot provides an open-source MCP platform including gateway, catalog, chat client, and agent orchestration. The platform supports both self-hosted deployment and a managed hosted MCP Gateway for teams that do not want to operate the environment themselves.
What Makes Obot Different
Obot includes a built-in MCP catalog with auto-documentation and discovery. Obot includes an agent orchestration framework on top of MCP connectivity. Verify current framework name and capabilities at obot.ai.
Key Capabilities
- Self-hosted deployment with Docker or Kubernetes, plus a managed hosted MCP Gateway option
- Built-in catalog with discovery
- Enterprise identity provider support
- Advanced agent orchestration framework
Tradeoffs to Consider
Obot is OSS-first and supports self-hosting with Docker for development and Kubernetes for production, while also offering a managed hosted MCP Gateway. Teams comparing it with MintMCP should evaluate differences in SCIM-driven RBAC, Virtual MCPs, Agent Bundles, hosted connector operations, and centralized observability.
Best For: Startups with Kubernetes expertise wanting maximum customization.
Pricing: Self-hosted open source is free; managed cloud and enterprise options are available.
8. Lasso Security
Lasso Security's MCP Gateway offers built-in threat detection and prevention. The platform analyzes MCP server reputation and provides real-time security scanning.
What Makes Lasso Different
The gateway blocks risky tools automatically through reputation scoring. Real-time threat detection catches prompt injection and PII leakage. Verify current integration details at the Lasso Security repository.
Key Capabilities
- Real-time threat detection for security risks
- MCP server reputation scoring
- Plugin architecture for security guardrails
- PII masking and redaction
- Recognition as Gartner Cool Vendor for AI Security (as of 2024; verify current status)
Tradeoffs to Consider
Lasso Security is strongest where MCP security scanning and threat detection are primary requirements. Startups should also evaluate whether they need MintMCP's SSO and SCIM-driven RBAC, Virtual MCPs, Agent Bundles, hosted connectors, tool-update policy, and complete audit trails for internal employee and agent governance.
Best For: Security-conscious startups handling sensitive data.
Pricing: MIT license (verify current licensing terms).
9. Portkey
Portkey provides AI infrastructure connecting to a large catalog of LLMs through a single API while adding MCP gateway capabilities. The platform consolidates model access, observability, and tool orchestration.
What Makes Portkey Different
Beyond gateway functionality, Portkey includes observability, guardrails, prompt management, and caching in one platform. The architecture is designed for production reliability.
Key Capabilities
- Access to a broad catalog of language models (verify current count at portkey.ai)
- Built-in observability and guardrails
- Prompt management and caching
- SOC 2 Type II audited controls
Tradeoffs to Consider
Portkey is strongest as a broader AI gateway and developer platform. Startups that need MCP-specific internal governance should verify whether Portkey supports the primitives that matter for least-privilege MCP access, including Virtual MCPs, Agent Bundles with M2M auth, OAuth brokering for stdio and hosted servers, hosted MCP connectors, and centralized audit across employee and agent activity.
Best For: Startups wanting consolidated AI infrastructure.
Pricing: Free tier available; Production is $49/month; Enterprise pricing is custom.
10. IBM ContextForge
IBM ContextForge introduces federation architecture where multiple gateway instances can discover each other and share tool registries. This capability addresses distributed team requirements.
Note: IBM ContextForge does not appear in the approved competitive reference used for this guide. The capabilities below are based on publicly available documentation as of September 2026 and have not been independently verified against a current product reference.
What Makes ContextForge Different
The federation model enables coordinated gateway instances across regions. Virtual MCP servers may wrap legacy services for gradual migration. Verify current capabilities directly with IBM.
Key Capabilities
- Multi-gateway federation and discovery
- Protocol bridging for legacy APIs
- Multi-database support (verify current capabilities directly with IBM)
- Apache 2.0 open-source license
Tradeoffs to Consider
ContextForge is useful for technical teams with distributed gateway requirements. Startups should evaluate production readiness, deployment model, and operational requirements, especially if they need managed SaaS-first deployment, hosted MCP connectors, SSO and SCIM-driven RBAC, Virtual MCPs, Agent Bundles, and centralized audit logs.
Best For: Technical startups with advanced distributed requirements.
Pricing: Free and open-source.
Deploy Enterprise AI with Confidence
The Model Context Protocol has fundamentally changed how enterprises connect AI assistants to their data and tools. But deploying MCP at scale requires more than protocol support: it demands security, governance, and monitoring that transforms experimental AI into production-ready infrastructure.
MintMCP Gateway provides a governed path from pilot to production. With SOC 2 Type II audited controls, compliant with HIPAA standards, hosted connectors for enterprise data sources, SSO and SCIM-driven RBAC, Virtual MCPs, Agent Bundles, and an official Cursor Hooks partner listing, MintMCP addresses technical barriers including credential management, access control, and audit that can slow production deployment.
Whether you're securing access to Snowflake warehouses, Elasticsearch knowledge bases, or custom enterprise tools, MintMCP provides the infrastructure that makes AI deployment practical, auditable, and secure.
For a deeper understanding of MCP gateway architecture, see the guide to understanding MCP gateways. Review enterprise deployment guides for implementation planning based on your team's capabilities. For a security-focused checklist, see the MCP security checklist.
Ready to transform your AI infrastructure? Visit mintmcp.com to schedule a demo and see how MintMCP Gateway can accelerate your enterprise AI deployment.
Frequently Asked Questions
What is an MCP gateway and why do startups need one?
An MCP gateway sits between AI agents and the tools they access, including databases, APIs, and internal systems. Without a gateway, each connection requires custom authentication, lacks audit trails, and creates security vulnerabilities. Gateways centralize authentication, monitoring, rate limiting, and compliance so teams focus on building AI features rather than infrastructure. Learn more about MCP gateway architecture.
How quickly can I deploy an MCP Gateway?
Deployment speed varies by platform. Some solutions achieve setup in under 30 seconds for basic configurations. Docker-based approaches work immediately for teams with existing container infrastructure. Managed platforms like MintMCP are designed to reduce time-to-deployment compared to self-hosted options; verify current setup timelines at mintmcp.com. Enterprise platforms with SSO integration may require 2 to 4 weeks for full configuration.
Which gateway should I choose if compliance is mandatory?
MintMCP is a SOC 2 Type II audited MCP platform with continuous compliance monitoring via Drata. For startups selling to regulated industries, this can reduce security review friction while giving IT and security teams centralized audit trails, SSO, RBAC, and tool-level access controls. Customers handling protected health information can request HIPAA documentation, and MintMCP signs BAAs.
What's the difference between an MCP gateway and an agent gateway?
An MCP gateway governs which tools and data an AI system can access, handling authentication, credentials, access control, and audit for tool connections. An agent gateway builds on that foundation by giving each autonomous agent its own identity, scoped permissions, and credentials, so agents can be independently audited, rotated, and revoked without touching human accounts. MintMCP's Agent Gateway extends its MCP Gateway with per-agent agent identities, M2M authentication, and workload identity federation.
What's the difference between MCP and LLM Gateways?
LLM gateways route requests between applications and language model providers, handling authentication and rate limiting for model API calls. MCP gateways manage connections between AI agents and tools or data sources. Some platforms combine both functions. For coding agent monitoring specifically, see MintMCP's Agent Monitor.
How do I monitor AI agent activities?
Gateway platforms provide varying levels of observability. MintMCP tracks every tool call with complete audit trails for compliance. Its Gateway plus Agent Monitor model covers MCP traffic as well as supported local non-MCP coding-agent activity, including off-gateway use in Cursor and Claude Code. Others offer real-time metrics and logging, while security-focused options add threat detection monitoring.
How do I prevent MCP configuration sprawl across my team?
Configuration sprawl happens when each developer configures MCP servers independently on their own machines. A Virtual MCP solves this by bundling approved connectors and a curated tool surface behind one governed endpoint. Team members connect once; access is controlled centrally through SSO and SCIM-driven groups. MintMCP's Virtual MCP model lets you create separate endpoints for different teams, roles, or agents without requiring individual setup on every machine.