Composio is a developer integration platform that gives AI agents access to pre-built tool connections for popular applications. It is designed for developers building agent applications quickly. Its current Enterprise offering also includes managed credential handling, SSO and SCIM, role-based and action-level permissions, audit trails, and self-hosting. Enterprise teams seeking a governance layer centered specifically on internal employee and autonomous-agent access may still prefer a different architecture.
This guide examines the top Composio alternatives, with particular focus on why MintMCP's MCP Gateway is a strong fit for regulated industries and security-conscious organizations.
Key Takeaways
- MintMCP is built for enterprise AI agent governance with a data-permissions-first architecture, SSO and SCIM-driven RBAC, Virtual MCPs, Agent Bundles, tool-level allowlisting, three-layer guardrails, audit logs, and centralized observability
- Composio remains primarily developer- and AI engineering-oriented but now includes enterprise governance controls, so enterprise teams should compare its agent-application governance model with their requirements for internal employee and autonomous-agent governance
- Deployment models vary significantly: MintMCP is managed SaaS-first, while some alternatives prioritize open-source, embedded, or self-hosted integration models
- Governance depth is the main evaluation factor: compare each platform's support for tool-level policy, credential management, auditability, identity-based access, and agent monitoring
- Consider the primary use case: choose MintMCP for internal enterprise governance, Composio for developer-led agent integration with enterprise controls, Nango for open-source and self-hostable integration infrastructure, or Merge Agent Handler for MCP tool calling with Tool Packs, security controls, and auditability
Where Composio Hits Its Ceiling for Enterprise Teams
Composio serves developer-led teams well with its toolkit library and rapid onboarding, and its Enterprise offering now includes meaningful governance capabilities. Organizations evaluating Composio against internal governance requirements should therefore compare architectural differences rather than assume those controls are absent:
- Composio provides managed OAuth and centralized credential storage, including automatic token refresh for supported OAuth connections. MintMCP differs by tying governed credentials to its broader Virtual MCP and Agent Bundle access model.
- Composio supports SSO, SCIM, role-based permissions, and action-level access controls. MintMCP's model centers SCIM-driven membership around Virtual MCPs that define curated tool surfaces for internal teams, roles, use cases, and agents.
- Composio's identity and authorization model organizes agent activity around users, sessions, teams, and action permissions, while MintMCP's Agent Bundles explicitly model autonomous agents as first-class non-human identities with independently rotatable and revocable credentials.
- Composio provides audit trails and tool-execution logs for tracing agent activity. MintMCP combines MCP Gateway auditability with tamper-evident access history and Agent Monitor visibility across supported off-gateway agent activity.
- Composio now provides an enterprise governance surface alongside its developer-first integration model. MintMCP is positioned more specifically as a central IT, security, and AI operations control layer for internal AI clients and autonomous agents.
- Compliance mandates should be evaluated against current attestations, deployment controls, and security architecture rather than inferred from product category. Composio's current Enterprise offering includes SOC 2 Type II and ISO 27001 controls, while MintMCP is SOC 2 Type II audited, compliant with HIPAA standards, and offers BAAs. Organizations should map these capabilities to their own requirements and relevant federal cybersecurity standards
Organizations in regulated industries often find that the governance layer needs to be a platform feature, not something built on top after the fact. That is the architectural distinction these alternatives address.
Understanding Composio
Composio's Primary Focus
- Pre-built toolkits spanning productivity, development, and communication applications
- Native support for LangChain, CrewAI, AutoGen, and LlamaIndex frameworks
- Managed OAuth handling and centralized credential storage that simplify authentication flows
- SDK-first approach enabling rapid agent development
Common Reasons Teams Seek Alternatives
Enterprise teams are no longer choosing alternatives simply because Composio lacks centralized credentials or auditability. Composio now provides managed credentials, tool-level permissions, enterprise identity controls, and tool-execution logs. The more relevant decision is whether an organization needs a governance architecture centered on internal AI clients, first-class non-human agent identities, role-specific MCP endpoints, and visibility beyond tool calls routed through the integration layer.
Other common drivers include:
- Enterprise governance requirements centered on internal employee and autonomous-agent access
- Need for first-class non-human identities with independently rotatable and revocable agent credentials
- Compliance mandates requiring SOC 2, compliance with HIPAA standards, BAA availability, or enterprise security frameworks
- Desire for curated MCP endpoints to control approved tool access by team, role, or use case
- Requirements for real-time agent monitoring and policy enforcement beyond routed integration calls
Real operational pain behind these requirements often sounds like this:
- "It's annoying to manage API integrations and MCPs across multiple computers... there's gotta be a better way." This is the config sprawl problem that Virtual MCPs solve by centralizing access behind a single governed endpoint.
- "Non-technical users say 'go do something' and Claude runs curl -L to a random site piped to sh... they can install malicious things from the AI." This is the dangerous agent action problem that Mint Guard and Agent Monitor rules address at runtime.
- "I don't want to be the single point of failure if my account freezes." This is the shared-credential problem that per-agent identity and independent credential revocation solve through Agent Bundles.
1. MintMCP: Best for Enterprise AI Agent Governance
MintMCP provides enterprise MCP infrastructure designed for IT, security, and AI operations teams deploying AI agents at scale. As part of the Cursor Hooks Partners Program, MintMCP supports Cursor integration with governance and visibility controls.
Composio remains developer-first and now includes substantial enterprise governance capabilities. MintMCP is built around internal organizational governance. The difference is emphasis: Composio provides developers with a managed action and integration layer for agents and applications; MintMCP gives security and platform teams a control layer over what internal AI systems can access, which identities and credentials they use, and what activity is attributable to them.
Key MintMCP Advantages
- SOC 2 Type II audited security controls and compliance with HIPAA standards, with BAA availability for enterprise security review requirements
- Data-permissions-first architecture built around SSO, SCIM, IdP groups, Virtual MCPs, tool-level policy, and audit
- Virtual MCPs enabling organizations to create per-use-case endpoints with SCIM-driven membership, curated tools, and access policy
- Agent Bundles with per-agent identity, bearer keys, M2M OAuth tokens, workload identity federation, and "act as agent" flows; each agent's credentials are independently rotatable and revocable without touching human accounts
- Tool-level allowlisting and three-layer guardrails for centralized control over approved tools and runtime policy enforcement
- Audit logs and centralized observability for compliance review, with SIEM export for centralized security visibility across agent activity
Enterprise Security Features
MintMCP's security architecture provides centralized governance across all AI agent deployments:
- SSO and SCIM-driven RBAC
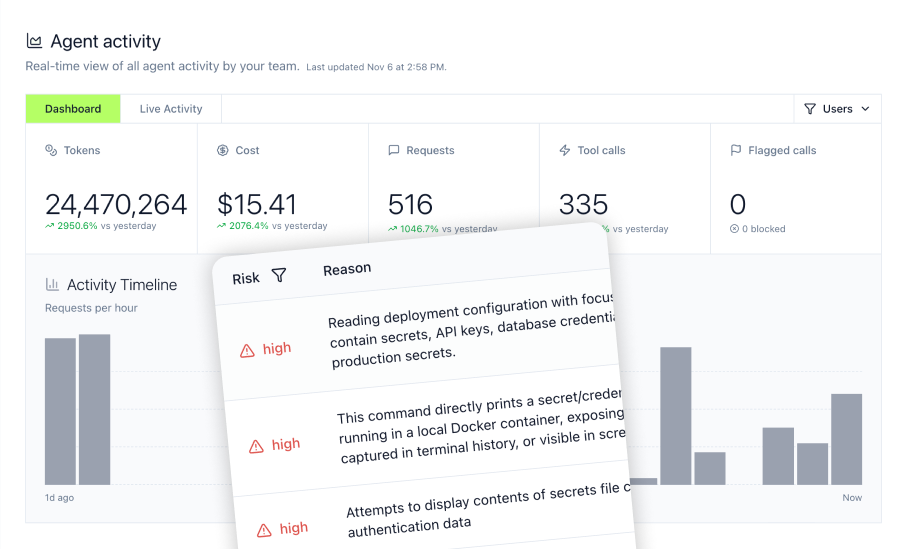
- Two-layer visibility: MCP Gateway governs traffic through governed MCP connections; Agent Monitor sees agent activity beyond gateway traffic, including prompts, commands, file access, and MCP tool calls from Claude Code, Cursor, Codex, and Copilot, with Agent Monitor rules for flag, block, ask, mask, or notify actions, plus SIEM export for centralized security visibility
- Granular tool access control by role, use case, and agent identity
- Three-layer guardrails: Mint Guard for managed detection of prompt injection, secrets, and PII (Off, Monitoring, and Enforcing modes); Rules for declarative matching and enforcement; Gateway Middleware for customer-authored JS logic including external DLP integrations
- Credential management and OAuth brokering for STDIO and hosted MCP servers
- Tool-update policy to approve or block new upstream tool versions before they reach agents
- Organization-wide and tool-level shutdown controls for immediate response if an agent or connector needs to be taken offline
Coworker Agents: Governed Autonomous Work, Not Just Tool Access
For teams that need agents to work continuously, not just respond to prompts, MintMCP's Coworker Agents run as long-running agents alongside employees. They operate through Slack, scheduled triggers, or manual runs; retain company-owned memory that stays reviewable, versioned, and auditable; and use scoped tool access with governed credentials. Instructions, memory, and work history remain under organizational control rather than inside an opaque vendor system.
MintMCP extends its governance model beyond integration access into hosted, long-running Coworker Agents that can work across days with company-owned memory and governed tools.
Ideal Use Cases
- Healthcare organizations requiring strong audit trails and documented security controls (see security teams)
- Financial services firms needing audit-ready compliance infrastructure
- Teams that need governed AI deployments with clear security review workflows (see engineering teams)
- Any organization where IT and security teams need centralized oversight
Integration Capabilities
MintMCP supports direct connections to enterprise data sources through dedicated connectors:
- Elasticsearch integration for AI-powered knowledge base search
- Snowflake connector enabling natural language queries against data warehouses
- Gmail integration for AI-assisted email workflows with security oversight
- Support for Claude, ChatGPT, Gemini, Microsoft Copilot, Cursor, and other supported MCP clients
The Agent Monitor component provides additional visibility into local agent behavior, including non-MCP coding-agent activity, while the gateway governs MCP traffic, policy, tool access, and audit logging.
2. Nango
Nango is an integration platform with open-source components, a managed cloud offering, and Enterprise self-hosting and BYOC options. It supports tool calling for AI agents through action functions and a built-in MCP server, alongside managed authentication, syncs, webhooks, logs, and OpenTelemetry export.
Nango's Primary Focus
- Developer-focused integration infrastructure for external APIs, including managed authentication, pre-built and customizable functions, data synchronization, webhooks, and MCP-based agent tool calling
Considerations
Nango gives teams substantial implementation control and now includes Enterprise capabilities such as RBAC, SCIM, SAML SSO, audit trails, OpenTelemetry export, and self-hosting or BYOC. Its access model is centered on integrations, environments, user connections, and scoped action functions. Teams evaluating it for internal AI governance should compare that model with MintMCP's SCIM-driven Virtual MCPs, first-class non-human Agent Bundles, runtime guardrails, and Agent Monitor coverage.
3. Arcade
Arcade is an actions runtime for AI agents that combines managed tool authentication and execution with MCP gateways, identity integration, access controls, audit logging, and agent lifecycle governance. It supports Arcade Cloud, cloud marketplace deployment, and self-hosting with Helm.
Arcade's Primary Focus
- Secure agent-to-tool execution with managed authentication, MCP gateways, OIDC user identity, Contextual Access controls, audit logging, and centrally governed tool access
Considerations
Arcade now overlaps directly with enterprise MCP governance rather than serving only as an authentication runtime. Teams evaluating Arcade and MintMCP should compare Arcade's MCP Gateway, User Sources, Contextual Access, lifecycle governance, and audit model with MintMCP's Virtual MCPs, Agent Bundles, SCIM-driven access, three-layer guardrails, Agent Monitor, and Coworker Agents.
4. Merge Agent Handler
Merge Agent Handler is a tool-calling platform for AI agents, separate from Merge Unified. It exposes third-party tools through MCP and provides per-user or shared authentication, Tool Packs for scoped agent surfaces, a Security Gateway for data-loss prevention, audit trails, and enterprise identity controls.
Merge's Primary Focus
- MCP-based tool calling across third-party applications
- Per-user or shared authentication for connected accounts
- Tool Packs for defining and governing the tools available to an agent or user
- Security Gateway controls for PII, PHI, payment data, and custom matching rules
- Audit trails, SSO, SCIM, and custom roles for enterprise deployments
Considerations
Merge Agent Handler now overlaps materially with MCP-specific governance rather than serving only the unified API use case. Teams comparing it with MintMCP should evaluate Tool Packs, Registered User identity, Security Gateway controls, and auditability against MintMCP's Virtual MCPs, first-class Agent Bundles, tool-update policy, OAuth brokering, Agent Monitor, and broader internal agent-governance model.
5. Pipedream
Pipedream combines its established workflow automation platform with Pipedream Connect and MCP, which it now positions as an integration layer for AI agents. It provides managed authentication and hosted MCP access to pre-built tools across third-party APIs while retaining its visual workflow builder and code flexibility.
Pipedream's Primary Focus
- Managed integrations and authentication for AI agents and applications
- Hosted MCP access to pre-built third-party tools
- Visual workflow builder for no-code automation design
- Code flexibility when custom logic is required
Considerations
Pipedream now addresses AI-agent integration directly rather than focusing only on workflow automation. It also supports workspace SSO, SCIM, roles, and project access controls. Teams requiring internal AI governance should distinguish those workspace-level controls from capabilities such as MintMCP's SCIM-driven tool surfaces, first-class agent identities, runtime agent guardrails, tamper-evident access history, and cross-agent monitoring.
6. Paragon
Paragon serves the embedded integration market for B2B SaaS and AI products, enabling companies to offer native integrations within their products. Its ActionKit product exposes pre-built integration tools and triggers to AI agents through an API or MCP, alongside fully managed end-user authentication.
Paragon's Primary Focus
- Embedded integrations for B2B SaaS and AI product teams
- ActionKit tools and triggers for AI agents through API or MCP
- Managed end-user authentication for embedded integration experiences
Considerations
Paragon remains oriented toward embedded integration use cases rather than internal employee and autonomous-agent governance. Organizations deploying AI agents across their workforce should compare its connected-user and embedded integration model with requirements such as SCIM-driven tool access, first-class non-human identities, centralized MCP governance, runtime policy enforcement, and organization-wide agent observability.
How the Alternatives Compare
| Alternative | Primary buyer | Deployment | Per-agent identity | SCIM-driven RBAC | Audit trail | Guardrails | Coworker Agents |
|---|---|---|---|---|---|---|---|
| MintMCP | IT, Security, AI Operations | Managed SaaS-first; VPC/self-hosted on request | Yes (Agent Bundles with bearer keys, M2M tokens, workload identity federation) | Yes (SCIM-driven, IdP group membership) | Yes (tamper-evident, SIEM export) | Yes (Mint Guard, Rules, Gateway Middleware) | Yes (Slack, scheduled, manual triggers; company-owned memory) |
| Nango | Developers, platform engineering | Cloud; self-hosting and BYOC on Enterprise | User-scoped connections and agent action functions rather than MintMCP-style Agent Bundles | SCIM and RBAC available; workspace/environment access is managed separately from agent action scoping | Yes (audit trail, detailed logs, OpenTelemetry export) | Scoped action functions and integration permissions | Not a core product area |
| Arcade | Developers, platform operators | Arcade Cloud, cloud marketplace deployment, or self-hosted with Helm | Agent lifecycle governance with end-user identity through User Sources | OIDC User Sources and Contextual Access rather than MintMCP's Virtual MCP membership model | Yes (administrative and tool-execution auditability) | Yes (Contextual Access and policy integrations) | Not a core product area |
| Merge | Developers, product teams, enterprise agent teams | Managed service with US and EU endpoints | Tool Pack and Registered User scoping | Yes for enterprise team identity; Tool Packs govern agent tool surfaces | Yes (tool-call and administrative audit trails) | Yes (Security Gateway with allow, redact, and block controls) | Not a core product area |
| Pipedream | Developers, operations teams | Managed cloud; VPC options for workflows | User/project-oriented integration scoping | Workspace SSO and SCIM; project-level access controls | Workflow and execution history rather than a MintMCP-style agent audit model | Managed auth, tool exposure, and workflow controls | Not a core product area |
| Paragon | SaaS and AI product teams | Managed embedded platform; ActionKit also supports a self-hosted MCP implementation | Connected-user and embedded-product scoping | Team RBAC rather than MintMCP-style SCIM-driven agent tool membership | Monitoring and enterprise audit capabilities vary by deployment | Managed auth and embedded integration controls | Not a core product area |
Why MintMCP Is a Strong Fit for Enterprise AI Agent Governance
For organizations deploying AI agents in regulated environments, MintMCP centralizes tool access, agent identity, credentials, monitoring, and policy enforcement behind a governed control layer, so security teams can see supported agent activity and apply controls to risky actions.
The platform's SOC 2 Type II audited status, compliance with HIPAA standards, and BAA availability provide security review signals for compliance teams, while three-layer guardrails (Mint Guard, Rules, and Gateway Middleware) help prevent risky agent actions before they execute. With Virtual MCPs, security teams can curate exactly which tools their organization approves for each team, role, use case, or agent identity, reducing the risk of shadow AI deployments.
MintMCP's Virtual MCPs ensure that different teams see only the tools and data sources appropriate to their function. A finance team member accessing Claude Desktop through MintMCP will have a different set of available tools than an engineering team member, all managed centrally through the gateway with SCIM-driven membership and policy. This granular control, combined with audit logs and centralized observability, enables organizations to deploy AI agents confidently while maintaining visibility and oversight.
MintMCP's tool-update policy lets organizations approve or block new upstream tool versions before they reach agents, preventing unapproved tools from appearing in the tool surface without review. Organization-wide and tool-level shutdown controls give security teams an immediate response option if an agent or connector needs to be taken offline.
The platform integrates with enterprise authentication systems through SSO and SCIM-driven RBAC, allowing organizations to leverage existing identity infrastructure. Real-time monitoring through Agent Monitor provides security teams with visibility into supported agent behavior across the organization, while the gateway governs MCP traffic, credentials, policy, and tool access.
Organizations choose MintMCP when governance cannot be an afterthought. The managed SaaS-first deployment model reduces the amount of connector and governance infrastructure teams need to operate themselves, while still supporting VPC and self-hosted deployment on request for organizations with specific infrastructure requirements.
Frequently Asked Questions
What is the difference between Composio and an MCP gateway?
Composio is a developer-first managed integration and action layer for AI agents that supports SDK-based and MCP-based tool access, managed authentication, permissions, and enterprise governance controls. An MCP gateway like MintMCP is built specifically around governing MCP connections and internal AI-agent access across an organization. The categories now overlap, but MintMCP emphasizes Virtual MCPs, SCIM-driven internal access, first-class non-human agent identities, cross-agent monitoring, and runtime governance for IT and security teams.
Which Composio alternative is best for internal enterprise deployments?
MintMCP is purpose-built for internal enterprise deployments where IT and security teams need SCIM-driven RBAC, per-agent identities, Virtual MCPs, audit trails, and runtime guardrails as core platform features. Arcade and Merge Agent Handler also provide meaningful enterprise MCP governance capabilities, while Nango, Pipedream, and Paragon remain more integration-oriented in their primary product models.
Does MintMCP work with the same AI clients as Composio?
MintMCP supports Claude, ChatGPT, Gemini, Microsoft Copilot, Cursor, Windsurf, and custom agents through governed MCP endpoints. As part of the Cursor Hooks Partners Program, MintMCP supports Cursor integration with governance and visibility controls.
What governance capabilities does MintMCP provide?
MintMCP provides Virtual MCPs for per-use-case tool access, Agent Bundles for per-agent identity and credentials, three-layer guardrails (Mint Guard, Rules, and Gateway Middleware), Agent Monitor for visibility beyond gateway traffic, and SIEM export for centralized security visibility, all governed through SSO and SCIM-driven RBAC. The platform also provides centralized credential management and OAuth brokering for STDIO and hosted MCP servers.
Can migration from Composio to MintMCP be done?
Yes, migration is possible since both platforms support agent tool access workflows and MCP-compatible clients. MintMCP's hosted MCP connectors, Virtual MCPs, and policy framework can replace developer-led toolkit access with governed MCP endpoints. Migration timelines depend on integration complexity, security review requirements, and deployment scope.
How does MintMCP handle compliance requirements?
MintMCP is SOC 2 Type II audited and compliant with HIPAA standards, with BAA availability, tamper-evident audit trails, and SIEM export for centralized security visibility. Organizations in regulated industries can work with MintMCP during their security review process and access compliance documentation through the Trust Center.
How does MintMCP handle multi-team rollouts where different teams need different tool access?
MintMCP's Virtual MCPs let platform teams create separate governed endpoints for each team, role, or use case, each with its own curated tool surface, SCIM-driven membership, and access policy. A finance team and an engineering team can connect through the same gateway but see entirely different tool sets, all managed centrally without requiring per-user configuration on individual machines.
How quickly can enterprises deploy MintMCP?
MintMCP's managed SaaS-first model, hosted MCP connectors, and centralized policy controls reduce the amount of gateway and connector infrastructure organizations need to operate themselves. The platform handles OAuth, monitoring, and governance infrastructure. Organizations in regulated industries should allocate appropriate time for security review and compliance validation based on their specific requirements.